Digitalization
19. November 2026 5 min
Critical security flaw in NGINX: What it means for your website
On 18 November, two critical flaws in NGINX were made public. NGINX is software that runs on the servers behind millions of websites. The flaws can let an attacker take over the server without a login or password.
The short answer
Hosted with us? We closed the flaw the same day it was made public. Your website has not been affected, and you don’t need to do anything.
Hosted somewhere else? Ask your hosting provider today whether they have updated NGINX. Further down, you’ll find a checklist you can forward directly.
What is NGINX?
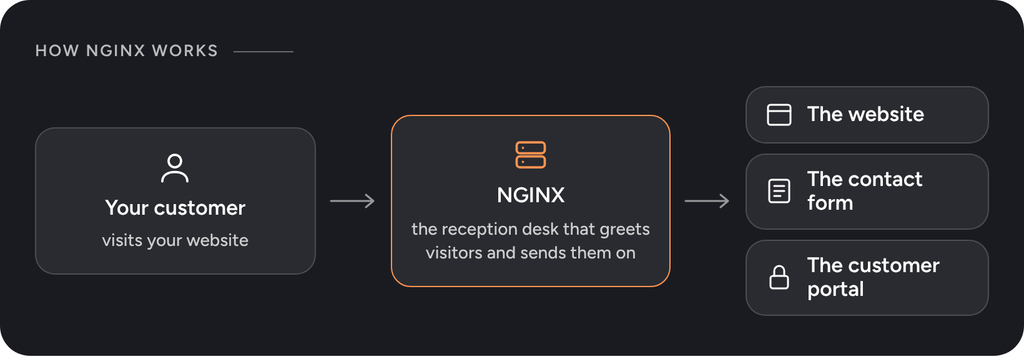
Think of NGINX as the reception desk at your company. When a customer visits your website, NGINX greets them and sends them on to the right page, form or customer portal. It happens in a split second, and nobody notices it as long as it works.
More than 225 million websites use NGINX. There’s a good chance yours is one of them.
What went wrong?
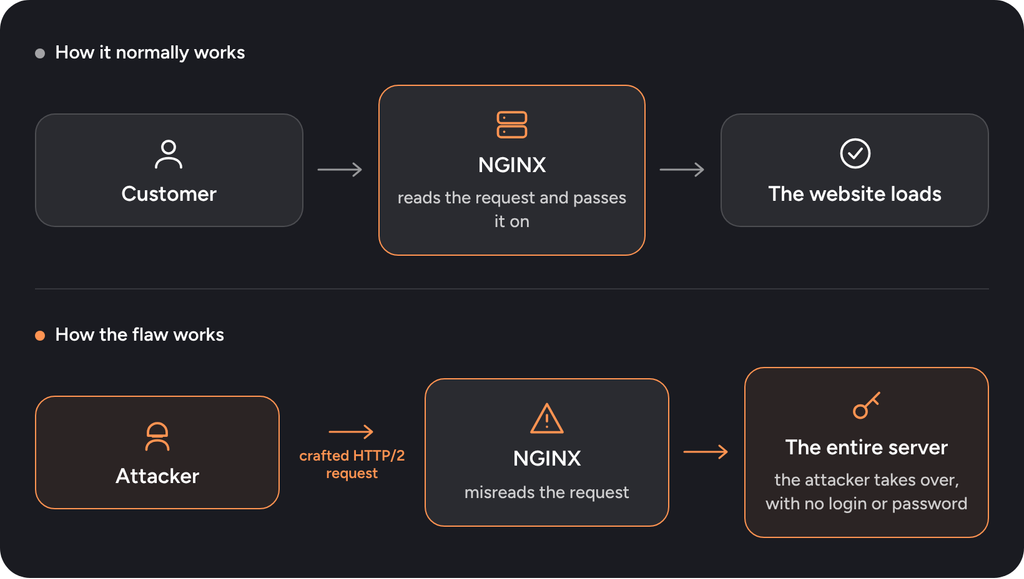
The flaws are in the way NGINX handles HTTP/2. HTTP/2 is the fast version of the connection between the browser and the server, and it’s switched on for most modern websites.
An attacker can send a specially crafted request to the server. NGINX misreads it, and the attacker can then run their own code on the server. It’s like a stranger walking in through the front door, handing the receptionist a note and leaving with the keys to the entire building.
What matters is where the flaw sits: in NGINX, not in your website. So it doesn’t help that your website is up to date and secure. If the reception desk hands out the keys, it doesn’t matter how well the offices are locked.
The flaw has been hidden for over ten years
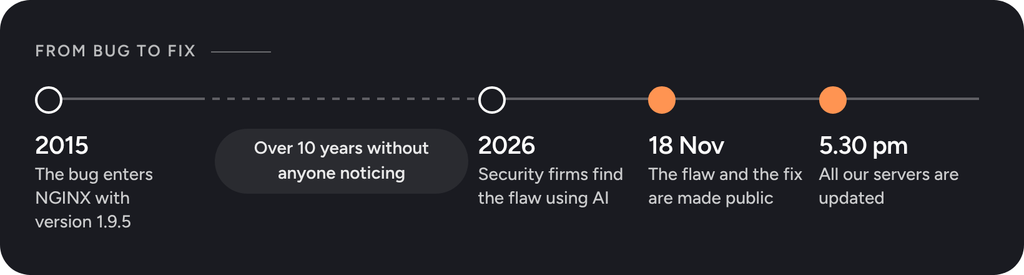
One of the flaws entered the code in 2015 and has been there ever since. This year, several security firms found it independently of each other, using AI to go through the code. One of the firms found four of the flaws in an hour and a half.
That’s good news and a warning at the same time. AI makes it faster to find bugs before anyone abuses them. But once a flaw is public, the time from discovery to attack gets shorter too. Security firm Rapid7 has already published code showing how the flaw can be exploited. That’s why the update has to happen now, not at the next scheduled maintenance window.
What could it mean for your sales?
Your website is often the first place a new customer meets you. It’s where buyers research your products before they get in touch, and where requests for quotes come in. If an attacker takes over the server, it hits your sales directly.
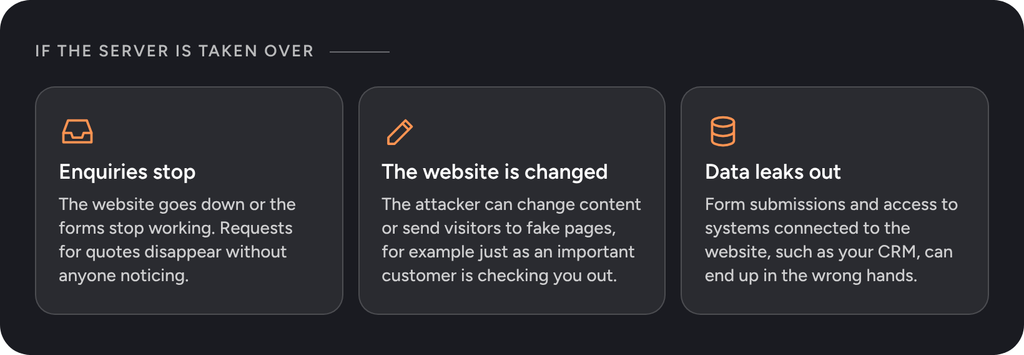
- Enquiries stop: The website goes down or the forms stop working. Requests for quotes disappear without anyone noticing.
- The website is changed: The attacker can change content or send visitors to fake pages, for example just as an important customer is checking you out.
- Data leaks out: Form submissions and access to systems connected to the website, such as your CRM, can end up in the wrong hands.
On top of that comes the clean-up: time to work out what happened, and time to win back the trust of the customers who noticed.
What should you do?
It depends on where your website is hosted.
Hosted with us? Then it’s fixed
We updated NGINX on all our servers on 18 November and were done by 5.30 pm, the same day the flaws were made public. Your website has not been affected, and you don’t need to do anything. If you have questions, contact your usual contact person at Morningtrain.
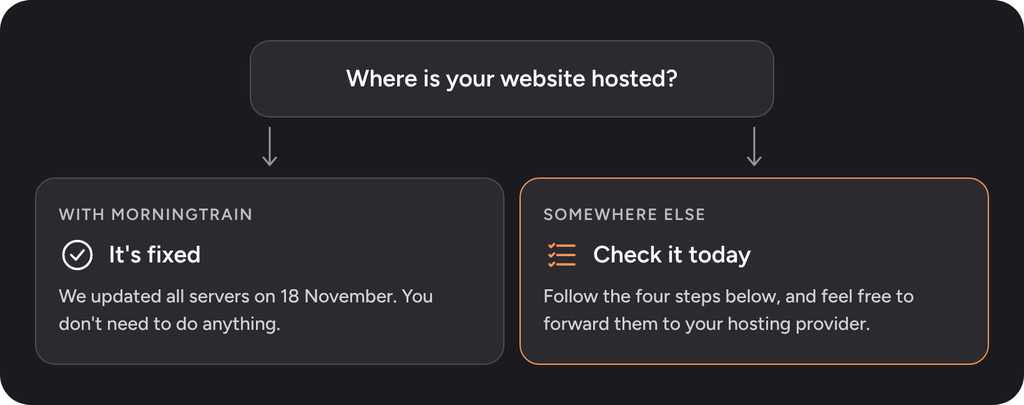
Hosted somewhere else? Here’s what to do
- Ask your hosting provider or IT department today. Ask whether your servers run NGINX and whether they have been updated to version 1.31.9 or 1.30.7 or later. Those are the versions where the flaws are closed. If they use NGINX from Ubuntu or Debian, for example, they should confirm that the latest security update is installed.
- Get the answer in writing. “We’re looking into it” isn’t an answer when the flaw is public. Ask for the date and time the update was installed.
- Remember the sites that are easy to forget. Campaign sites, customer portals, test sites and old domains that are still online often run on different servers than your main website.
- Call us if you’re unsure. We can quickly check whether your website is vulnerable and help you get it closed.
Sources: The Hacker News, CSO Online, Cybersecurity News and SQ Magazine.